

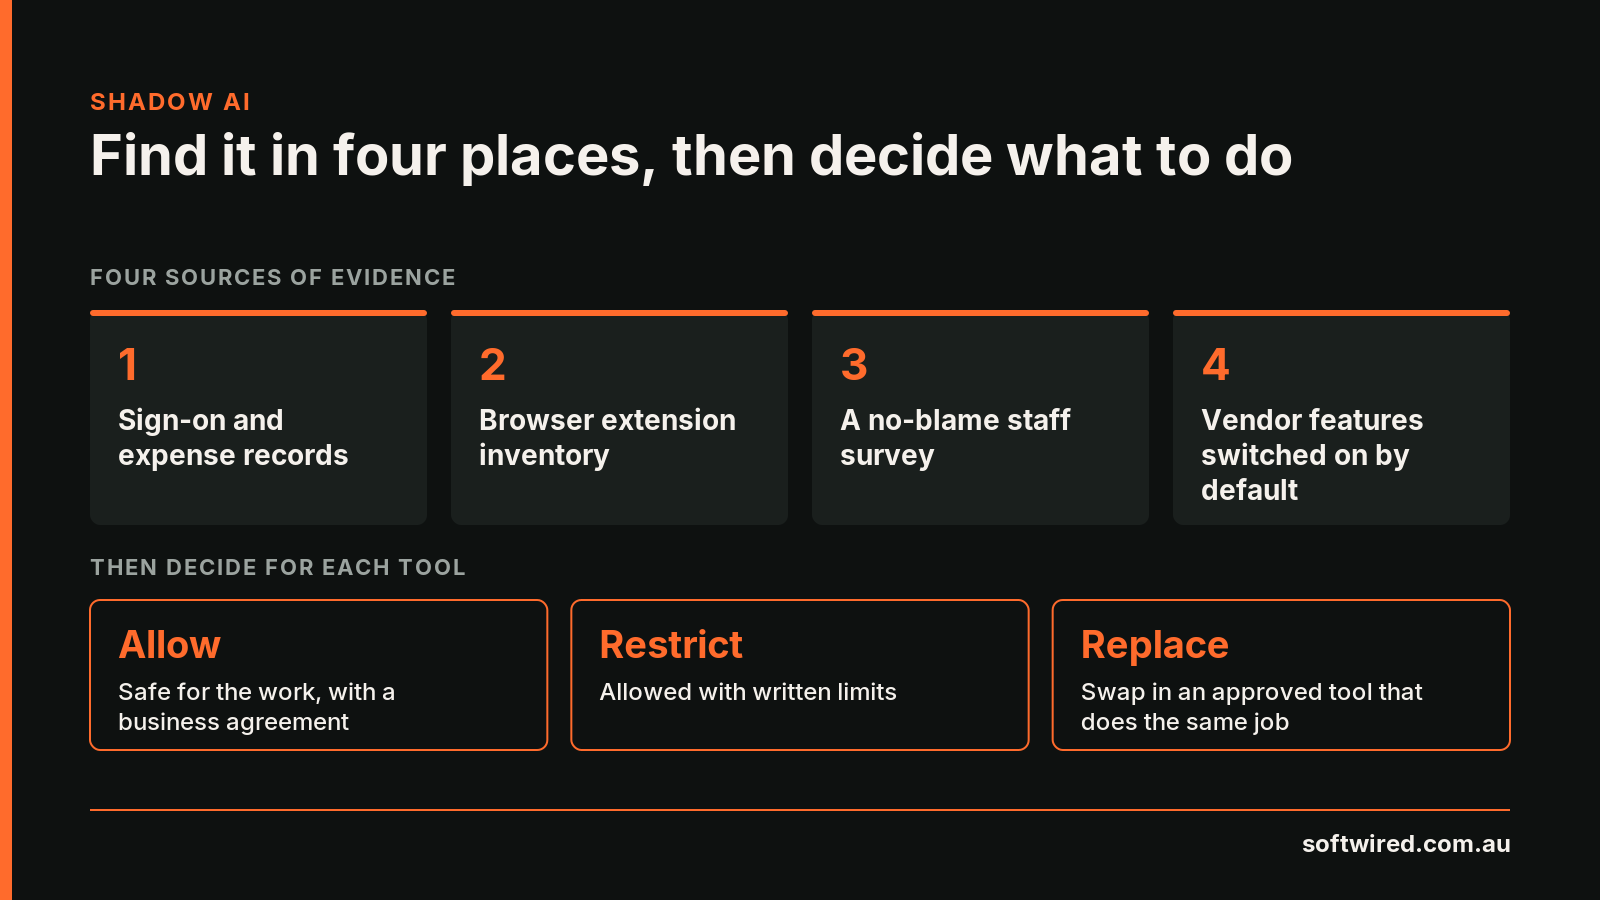
Shadow AI is the use of AI tools at work that the organisation can't see, approve or support. You find it by checking four sources of evidence, then deciding for each tool whether to allow it, restrict it or replace it.
Most shadow AI starts with good intentions. Someone on your team found a tool that writes a first draft in a minute, and nobody told them they couldn't use it. The aim of this method is to see what is happening and make sensible decisions about it, without turning it into a hunt. It is also the first step of AI Onramp, our AI adoption program.
Why shadow AI matters
Two risks sit behind it. The first is data leaving your systems. When a staff member pastes a client email into a personal AI account, that text now sits with a vendor you have no agreement with. The Office of the Australian Information Commissioner recommends that organisations do not enter personal information, "and particularly sensitive information", into publicly available generative AI tools (OAIC).
The second risk is decisions made on unchecked output. AI tools produce confident text that is sometimes wrong. If nobody knows a tool is in use, nobody knows to check what it wrote.
There is an opportunity in it too. Shadow AI tells you where staff already see value, which is useful when you choose a tool to back.
Four sources of evidence for shadow AI
Each source finds a different slice. Use all four, because each one misses something the others catch.
Sign-on and expense records
Your single sign-on logs show which AI tools staff have signed into with work accounts. Expense claims and corporate card statements show paid subscriptions, including ones bought on personal cards and claimed back. Together they give you the paid and work-account tools. They miss free tools used on personal accounts.
Browser extension inventory
Many AI tools arrive as browser extensions that can read whatever is on screen, including email and internal systems. If you manage browsers centrally, your IT team can list installed extensions. Look for writing assistants, meeting note-takers and summarisers. Check with your adviser before you monitor staff devices, because workplace surveillance rules vary by state.
A no-blame staff survey
Ask staff directly which AI tools they use and what they use them for. Offer an amnesty for past use and say so in the first line of the survey. Ask about the work, such as drafting, summarising, analysis or coding, as well as the tool. This is the only source that tells you why people use AI, and it finds the free personal-account tools the other sources miss. It works only if staff believe nobody will be punished for an honest answer.
Vendor features switched on by default
Some AI use is switched on by your software vendors. Our AI Feature Log records, for example, that ChatGPT access inside Word was on by default for ChatGPT Business workspaces from 1 October 2026, and that Docs Live in the Google Docs mobile app, announced 21 October 2026, is on by default for users with Gemini in Docs on eligible plans (entries read 28 October 2026). Check the admin settings of the software you already pay for. Our roundup of AI features switched on by default lists the current entries.
Allow, restrict or replace
Once you have the list, sort each tool into one of three groups.
- Allow: the tool is safe for the work people use it for, and you have, or can get, a business agreement with the vendor. Add it to an approved tools register.
- Restrict: the tool is fine for some work and wrong for other work. Allow it with written limits, for example no client or personal information.
- Replace: the tool does a useful job in an unsafe way. Give staff an approved tool that does the same job, then ask them to stop using the old one.
Banning tools without a replacement tends to push use further out of sight. Replacing them keeps the benefit and brings the work back where you can see it.
Write the outcome down. Our AI policy template shows how approved tools and data rules fit into a short policy, and our guide to AI advisory services explains who should own those decisions.
Frequently asked questions
What is shadow AI?
Shadow AI is the use of AI tools at work that the organisation can't see, approve or support. It includes personal accounts, browser extensions and AI features vendors switch on inside software you already use.
How do I find out which AI tools my staff are already using?
Check four sources: single sign-on logs and expense claims, a browser extension inventory, a no-blame staff survey with an amnesty for past use, and the admin settings for AI features your vendors switched on by default.
Should we ban AI tools we did not approve?
Banning without a replacement tends to push use out of sight. Sort each tool into allow, restrict or replace, and give staff an approved tool for the work they were already doing.
Is it legal to monitor which AI tools staff use?
That depends on your state and how you monitor, so check with your legal adviser before monitoring staff devices. A no-blame survey asks staff directly and avoids most of the question.
If you want help running this in your business, book a 30-minute call.
Want to talk through how this applies to your team? Book a call with Softwired.